Cyber P&L: Open-Source Cyber Risk Quantification
FAIR-style Monte Carlo loss modeling for cyber risk, control valuation, risk appetite, and CISO–CFO decisions.
Explore Cyber P&L →
CYBERSECURITY LEADERSHIP & ADVISORY
I was part of the founding team of the Microsoft Threat Intelligence Center, contributed early detections to Microsoft Sentinel, and led a detection engineering team in Microsoft Defender XDR. Across 18+ years, I have led security operations as both a provider and an enterprise practitioner. Today I advise CISOs on SOC strategy, detection engineering, incident readiness, cyber risk, and AI governance aligned with ISO/IEC 42001.

I specialize in real-world SOC operations, advanced detections, and rapid incident response – helping organizations identify, contain, and eliminate cyber threats before they escalate.

From data governance to secure architecture, I help teams strengthen privacy controls, reduce exposure, and meet modern security and compliance expectations without slowing innovation.

As a Certified Information Security Manager (CISM), Certified Information Systems Auditor (CISA), and Certified ISO/IEC 42001 Lead Implementer, I connect cybersecurity operations and AI governance with enterprise risk, compliance, audit, and business-focused decision-making.
I advise business leaders and strengthen security teams through practical cybersecurity strategy, risk guidance, and operational expertise.
THOUGHT LEADERSHIP
Original research and practical frameworks for security and risk leaders.
FAIR-style Monte Carlo loss modeling for cyber risk, control valuation, risk appetite, and CISO–CFO decisions.
Explore Cyber P&L →Why agent risk is governed through identity and authority, not model safety.
Read the research →An agent turns a hidden instruction in a vendor invoice into physical-system actions.
Read the research →Five reproducible experiments on containment authority.
Read the research →
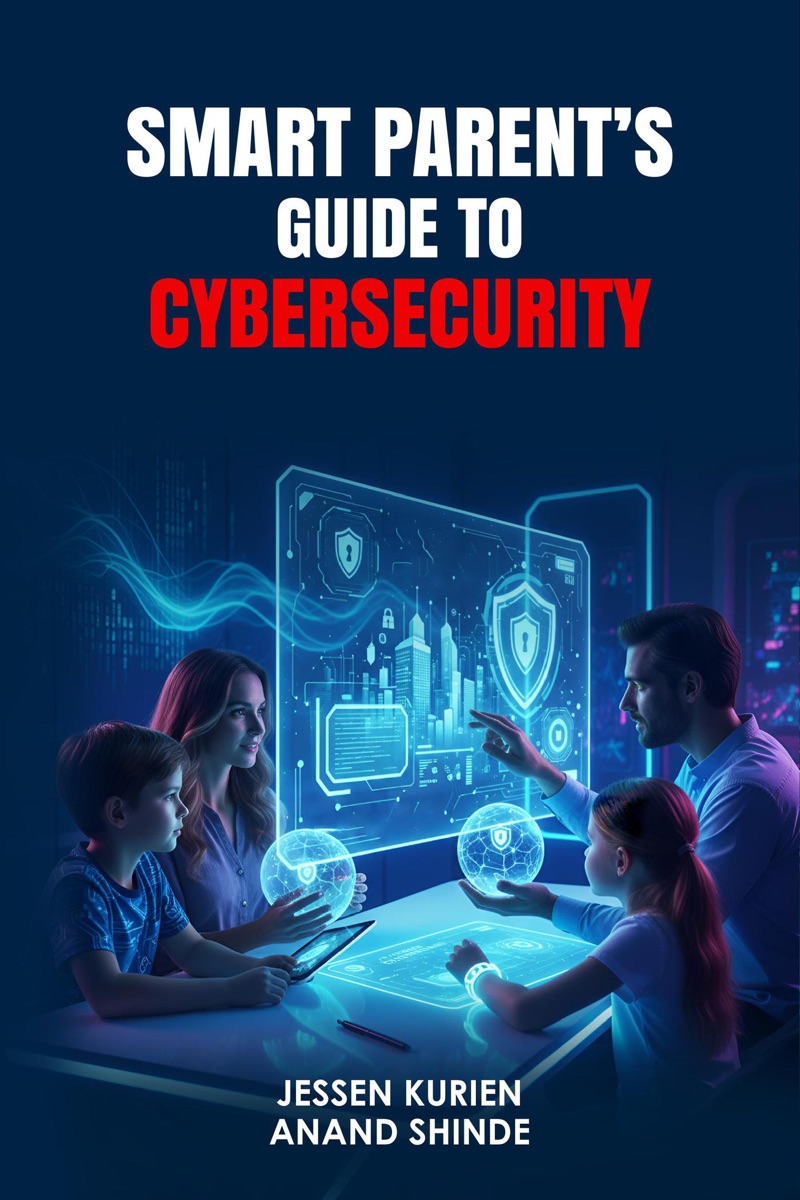
By Anand Shinde and Jessen Kurien · DevOM Publishing
Cybersecurity begins at home. Co-authored by Jessen Kurien and Anand Shinde, this practical guide helps parents and educators understand online threats, communicate clearly with children, and build safer digital habits without relying on fear.
The book also informs Jessen’s talks on digital safety, online responsibility, and cybersecurity careers for schools, colleges, families, and community audiences.
Delivering practical, enterprise-grade security solutions shaped by more than 18 years of frontline experience.

I provide clear, actionable cybersecurity insights grounded in hands-on operational experience — not theory or generic checklists.
From threat detection to incident response, I help teams strengthen security posture and respond with confidence.
Combining cybersecurity leadership with experience across eight Security Information and Event Management (SIEM) platforms, two Extended Detection and Response (XDR) platforms, and Security Orchestration, Automation and Response (SOAR), I advise enterprises on Security Operations Center (SOC) strategy, incident response, detection engineering, threat detection, cloud security, and risk-based vulnerability management. I help organizations strengthen cyber defense, accelerate response, reduce exposure, and align security operations with business risk and compliance priorities.
Core strengths include:
I combine executive-level cybersecurity advisory with practical implementation guidance to help organizations strengthen cyber resilience, reduce exposure, and achieve measurable security outcomes.
Featured research and practical tools: Cyber P&L for cyber risk quantification and security investment decisions, AI agent security and attack-path governance, cyber incident command and decision rights, and Microsoft Sentinel Defender portal transition readiness.

I help organizations assess, design, and mature Security Operations Center (SOC) capabilities, including operating models, workflows, detection coverage, metrics, technology strategy, and analyst enablement.
I help organizations prepare for and respond to complex cyber incidents through readiness assessments, incident command, investigation strategy, containment and recovery planning, executive communication, and post-incident improvement.
I help organizations identify, prioritize, and remediate risk across infrastructure, cloud, applications, and networks using vulnerability management, EASM, attack-path analysis, and remediation governance.
I help teams improve SIEM/XDR detection use cases, threat modeling, tuning, investigation workflows, SOAR automation, and responsible AI-assisted cyber defense.
I help leaders translate AI and cybersecurity risks into policies, controls, accountable ownership, measurable outcomes, and audit-ready evidence—supporting responsible AI adoption, ISO/IEC 42001 AIMS readiness, governance, risk and compliance (GRC), and operational resilience.
I deliver keynotes, workshops, executive briefings, university sessions, books, articles, and practical cybersecurity education for professional and public audiences.
Speaking audiences
Connect with Jessen about cybersecurity advisory, leadership opportunities, speaking engagements, books, research, or media. Share a little context to begin a focused conversation.